End-to-End Case Walkthrough

Follow one vulnerability from repository scan to verified closure.

Walk through a sample investigation (Case #Q-2026-0142) from start to finish: workspace isolation, Stage 0 secret redaction, cross-repository taint tracing, false-positive filtering across Gates A–H, and automatic Stage ∞ verification when the fix is merged.

Scroll to inspect each step
Step 1 of 5 · Workspace Isolation

Authenticate into an isolated tenant workspace.

Questor operates either as a multi-tenant cloud service with server-enforced query scoping or as a dedicated single-tenant instance inside your own private cloud. Every scan workspace, signing key, and database record is scoped strictly to your organisation.
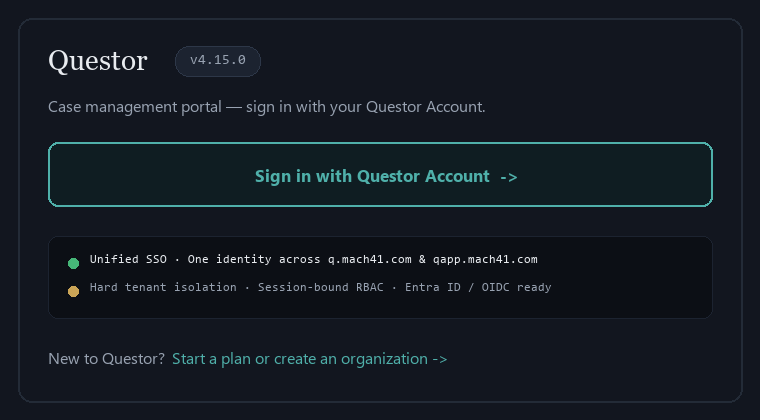
https://qapp.mach41.com/login
Sign in with Questor Account Single Sign-On
Questor Account SSO · Tenant-Scoped Access

Sign in with your Questor Account or enterprise Entra ID / Okta OIDC provider into four role-based permissions:

01 · Developer Starts repository scans, reviews source-to-sink traces, and responds to evidence requests.
02 · Defender / AppSec Reviews Gates A–H records, monitors disproven rates, and manages multi-repo portfolios.
03 · Decision-Maker Tracks financial risk exposure, SLA progress, and signed compliance packs.
04 · Workspace Admin Configures OIDC SSO, SCIM, model backends (Claude, Codex, Azure, Ollama), and Jira sync.
Tenant Security

Repositories, scan artifacts, and case records are strictly isolated per organisation across both cloud and private deployments.

Step 2 of 5 · Repository Intake & Secret Redaction

Connect a repository. Stage 0 strips credentials before analysis begins.

Enter a GitHub URL and select “Also scan related repositories”. Before any model prompt is built, deterministic Stage 0 redaction replaces keys, passwords, certificates, and .env secrets with typed placeholders.
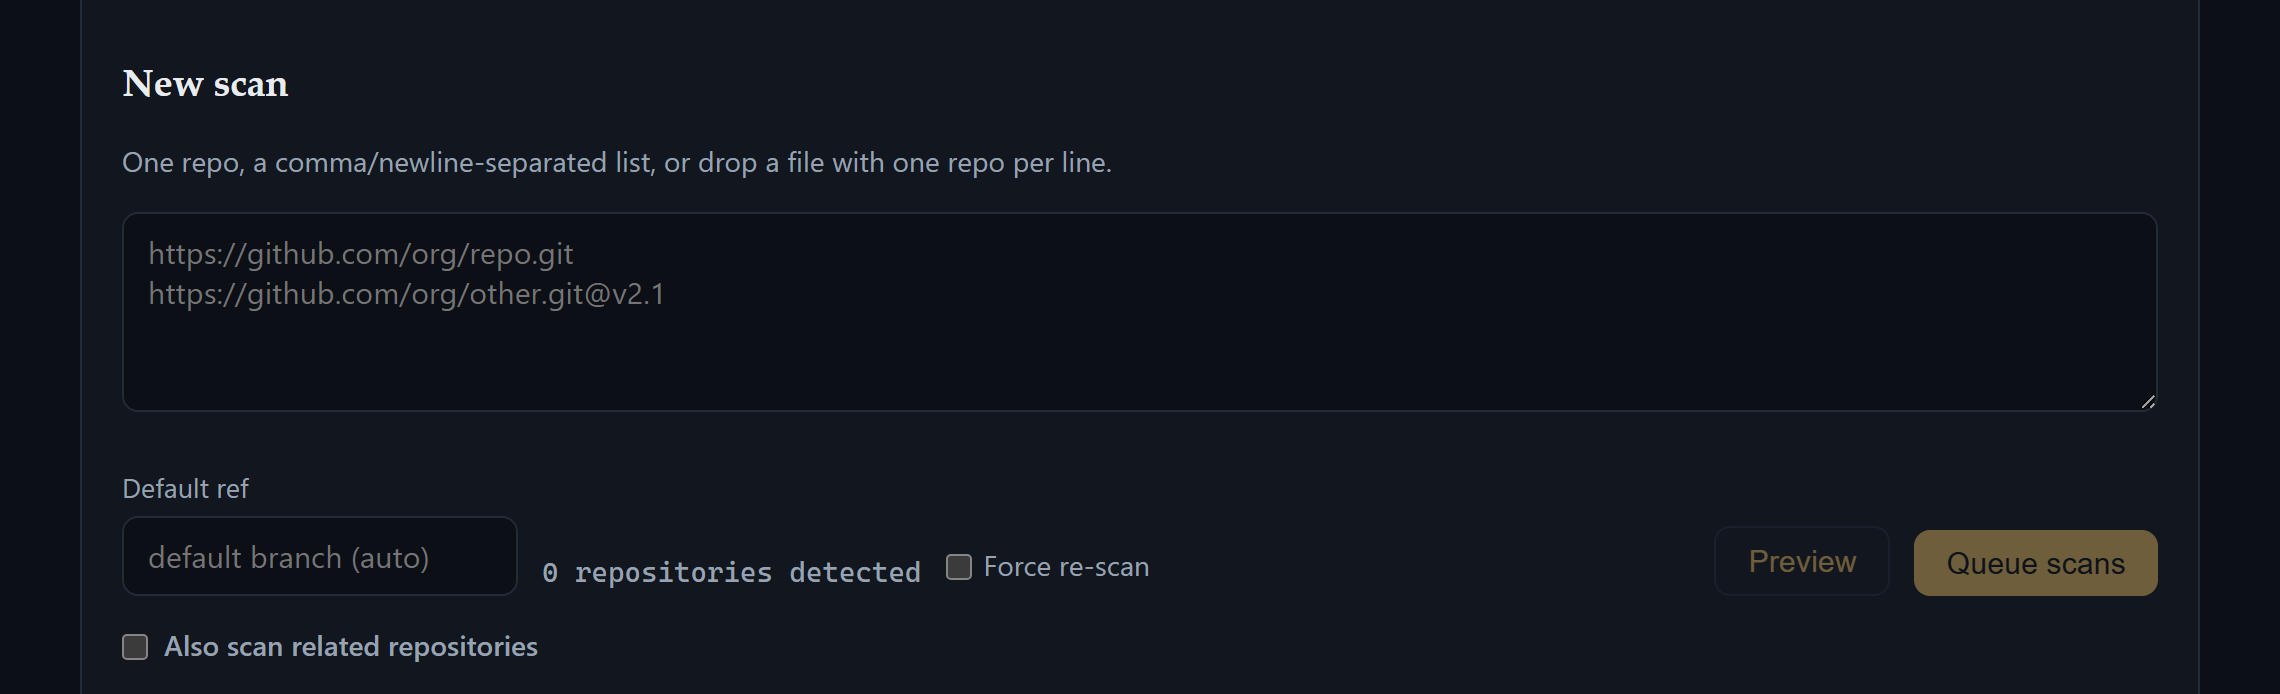
https://qapp.mach41.com/scans
The New-scan form - enter a repo URL, choose a ref, and scan related repositories
STAGE 0 · DETERMINISTIC SECRET REDACTION 14 SECRETS REDACTED ✓
// checkout-api/config/payments.env (Before Model Analysis)
- STRIPE_LIVE_SECRET="sk_live_51Nx98K2eZvKYlo2C981a..." + STRIPE_LIVE_SECRET="<REDACTED:stripe_secret_key:sk1a>" - DB_ADMIN_PASSWORD="Prod!Vault#99281_SqlPassword" + DB_ADMIN_PASSWORD="<REDACTED:generic_password:Prwd>"
✓ File structure & data-flow preserved · Raw credentials excluded from prompts
Read-Only Execution

Scans run in a strictly read-only sandbox with no repository writes, no target code execution, and Stage 0 credential redaction.

Step 3 of 5 · Cross-Repository Taint Analysis

Trace untrusted input across linked service repositories.

Questor catalogs entry points and sinks across the workspace, matching an outbound HTTP call in acme/api-gateway to its downstream handler and SQL sink in acme/orders-service. Select any repository node below to inspect the recorded trace:

Cross-Repo Taint Inspector · Click any node above

1. Source of Taint · acme/api-gateway (Entrypoint service repo)

Untrusted filter parameter enters GET /api/orders and is forwarded over an outbound HTTP request to the internal orders-service.

// api-gateway/src/routes/orders.js:18
export async function listOrders(req, res) {
  return http.get(`${ORDERS_SVC}/internal/orders?filter=${req.query.filter}`); // ← TAINT SOURCE
}
Step 4 of 5 · Gates A–H Validation

Every candidate is evaluated across Gates A–H before a case is marked Ready.

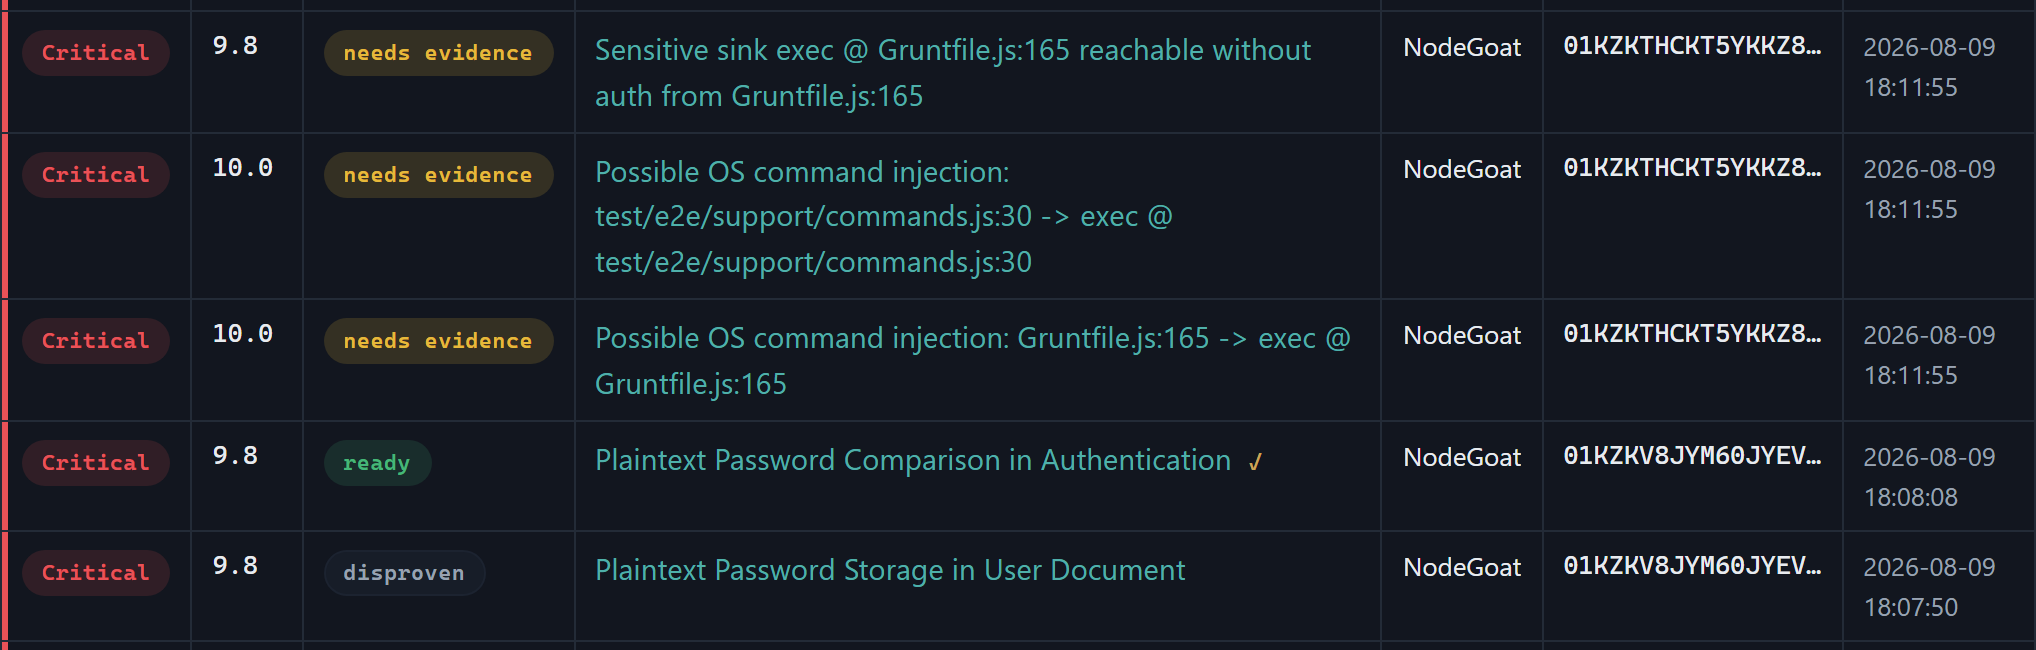
Initial model findings are treated as unverified hypotheses. Each candidate must pass eight validation checks. Confirmed findings are signed with Ed25519 as Ready; candidates refuted by guard checks or negative controls are logged as Disproven rather than sent to developers.
Gate AGrounding
Gate BReachability
Gate CSource→Sink
Gate DGuard & Class.
Gate EExploit Check
Gate FNeg Control
Gate GImpact
Gate H ✓Readiness Sign
https://qapp.mach41.com/cases
The Case Registry showing ready, disproven and needs-evidence statuses on NodeGoat findings
ready passed all 8 gates · verified for remediation disproven false positive ruled out at Gate D or Gate F needs evidence held pending a specific external config answer
AppSec Teams

Automated negative controls filter out false positives upstream while keeping a full audit log of every dismissed candidate.

Step 5 of 5 · Remediation & Stage ∞ Retest

Developers fix the pinpointed root cause, and Stage ∞ verifies closure.

Each Ready case provides the Ed25519-signed Gate A–H ledger, the exact source-to-sink file and line trace, and a static exploitability check. After the developer merges a fix, Stage ∞ re-scans the updated commit and signs the closure record.
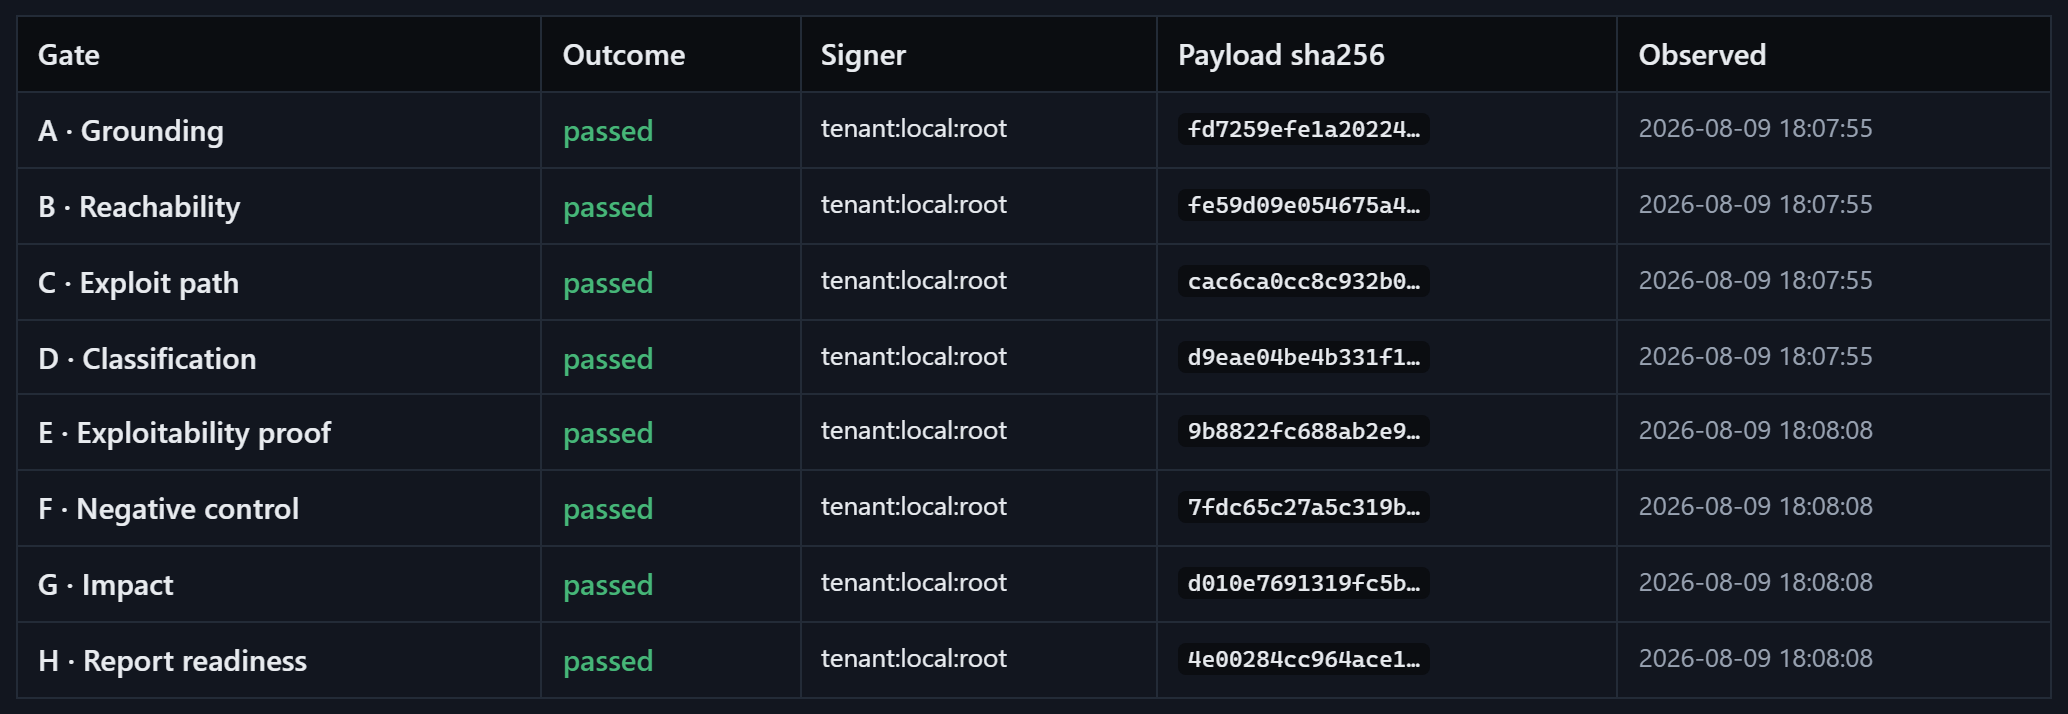
https://qapp.mach41.com/cases/Q-2026-0142#ledger
Signed gate ledger showing gates A to H passed and Ed25519-signed with payload hashes
✦ Developer PR committed against pinpointed sink · Verified on re-scan
// app/data/user-dao.js (Line 42 · pinpointed by Gate C)- if (received === user.password) {   // plaintext / weak compare+ if (await bcrypt.compare(received, user.password)) {    return authenticate(user);  }
Developer fix merged in PR #418 · Stage ∞ re-scan passed · Case Auto-Closed
↳ Full Cross-File Hop Chain (3 Hops)
Hop 1 [SOURCE] : routes/session.js:28   → req.body.password (untrusted HTTP POST)Hop 2 [PASS]   : services/auth.js:64    → validateCredentials(user, password)Hop 3 [SINK]   : app/data/user-dao.js:42 → direct comparison bypasses hash check
CWE-287 / OWASP A07 · Gate E static exploitability check signed
✓ Stage ∞ Drift Retest & Signed Closure
REMEDIATION    : REMEDIATED (Stage ∞ Drift Retest)COMMIT_SHA     : 94c10e8b2a7f4419d03e118aGATE_INF_CHECK : Prior source→sink path no longer reachableED25519_SIG    : sig:ed25519:7c419b02e88a41f09d3c...91a4
Audit ledger appended · Case #Q-2026-0142 marked Remediated
Engineering

Clear file-and-line root cause context up front, followed by automatic verification and case closure on re-scan.

Role-Based Views

One set of evidence across engineering, AppSec, and leadership.

The same signed case records power developer remediation, portfolio triage, and executive compliance reporting.

For developers

Fix verified vulnerabilities.

Every Ready case opens directly to the confirmed source-to-sink trace so engineers can verify the flaw in minutes and ship a fix.
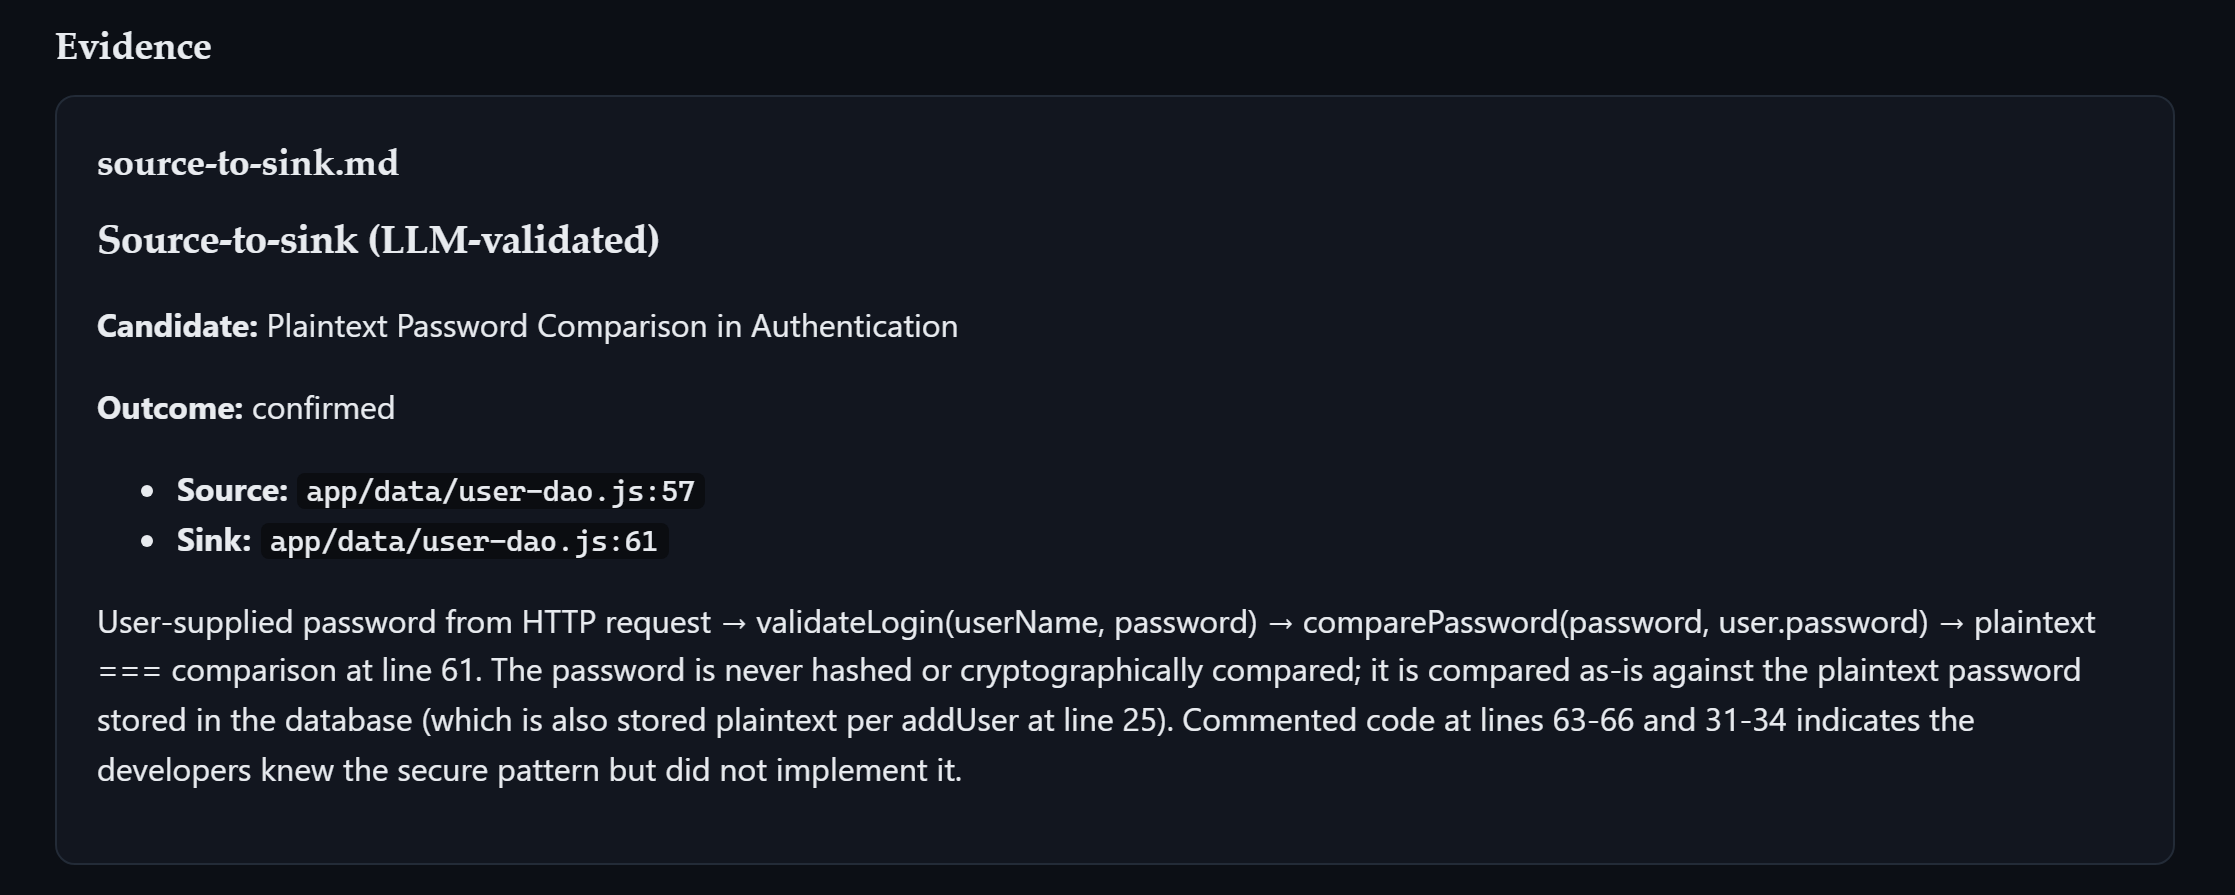
  • Filtered upstream: disproven candidates stay out of developer queues.
  • Complete context: source-to-sink path, static check, and calibrated impact.
  • Automatic closure: Stage ∞ re-scans commits and closes resolved cases.
https://qapp.mach41.com/cases/Q-2026-0142/evidence
Case evidence showing the validated source-to-sink path for a NodeGoat finding
For defenders

Measure precision across repositories.

Track proof rate, mean time to evidence, and the exact percentage of candidates disproven by negative controls across your portfolio.
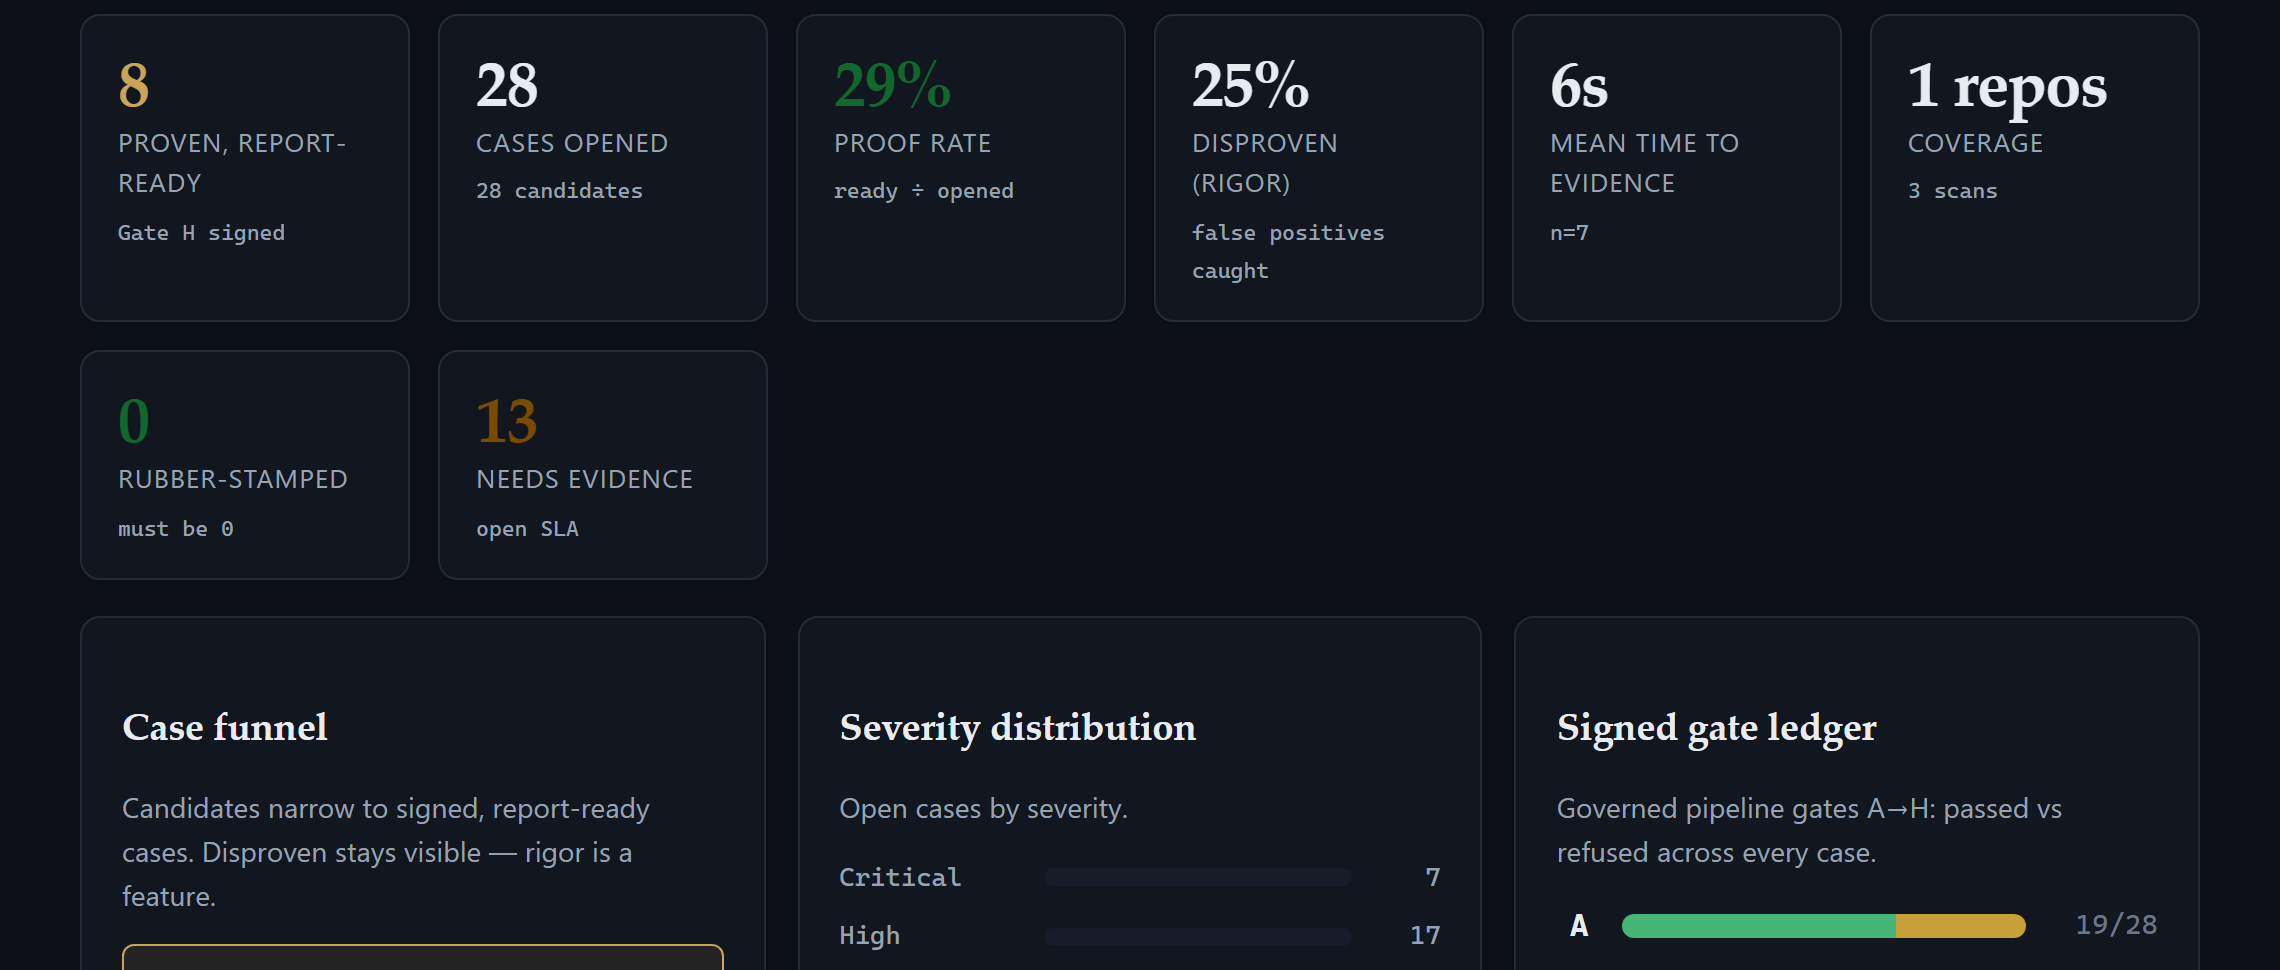
  • Proof & disproven rates tracked per repository and scan batch.
  • Zero unverified promotions: incomplete candidates are held for evidence.
  • Centralized governance: coverage metrics, SLA tracking, and Jira / SARIF sync.
https://qapp.mach41.com/analytics
Analytics view showing proof rate, disproven rate, and mean time to evidence
For decision-makers

Present audit-ready risk metrics.

Review quantified financial exposure and compliance status where every figure links directly to an Ed25519-signed case record.
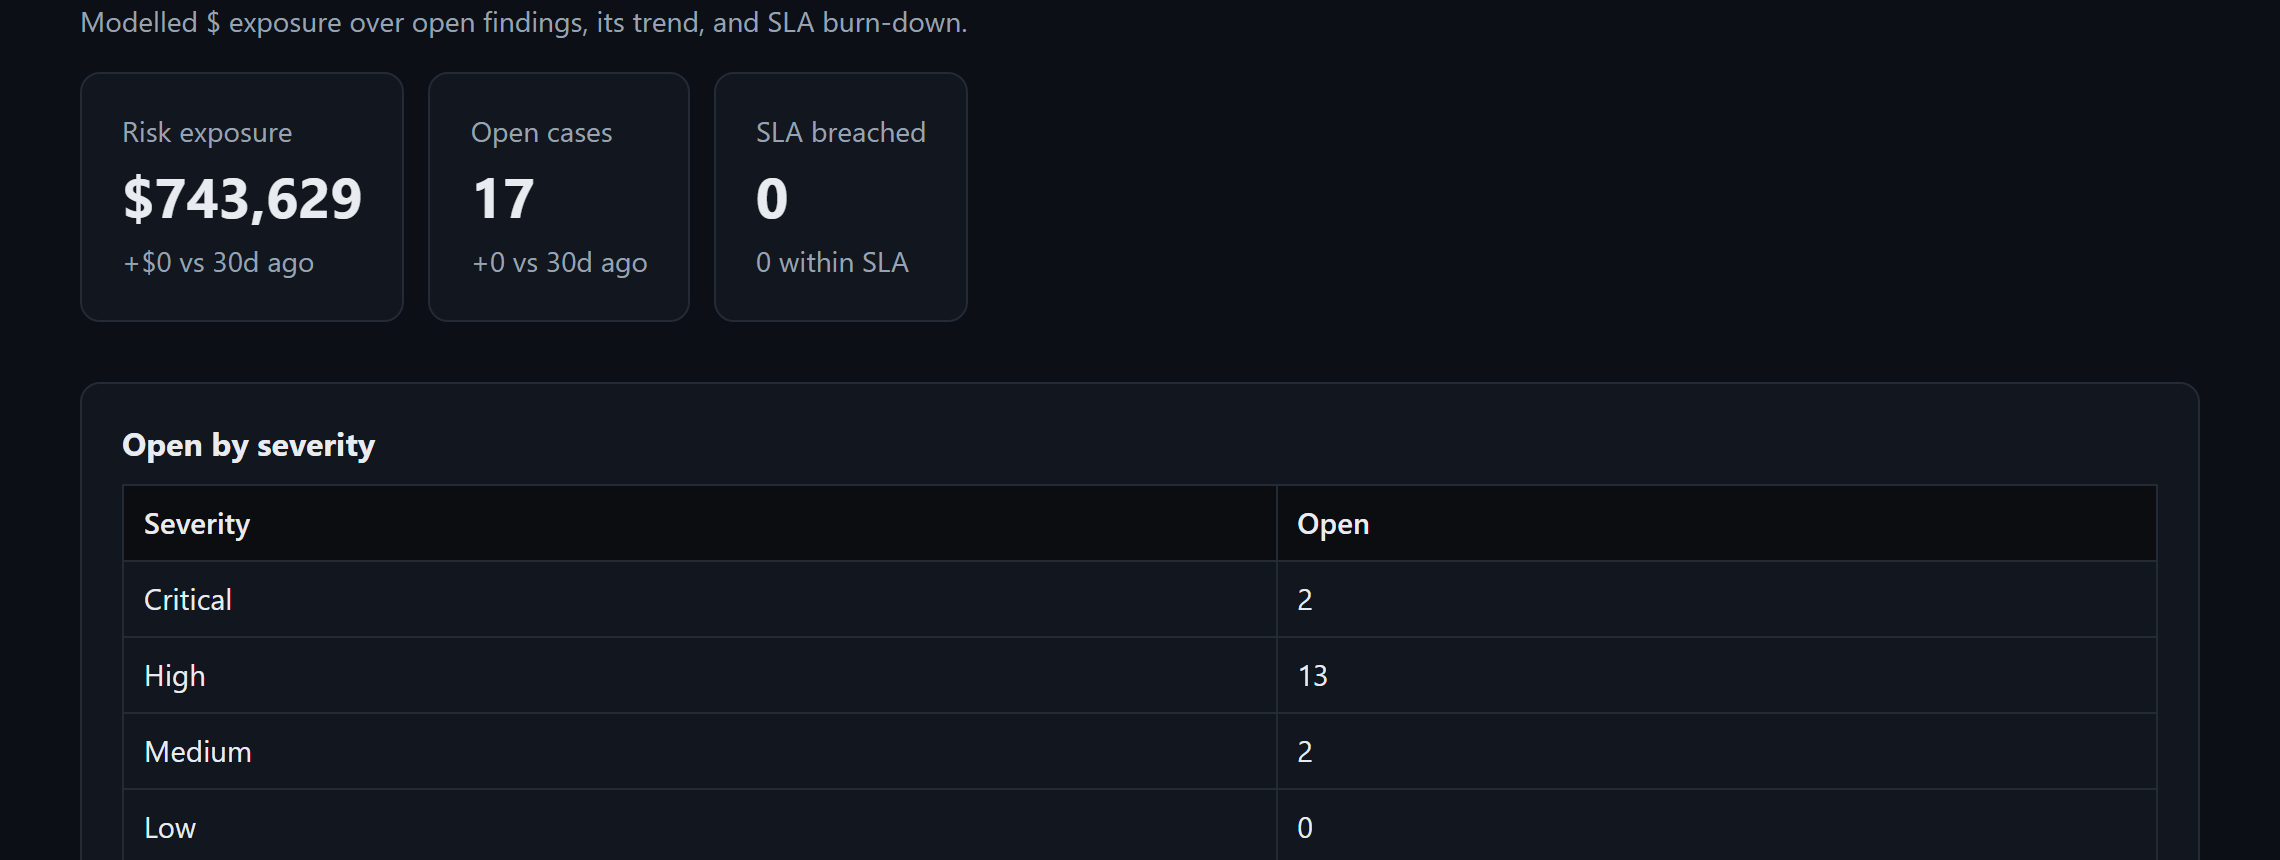
  • Modelled dollar risk exposure and remediation SLA burn-down.
  • Offline-verifiable Ed25519 signatures on every gate decision.
  • Framework mapping across SOC 2, ISO 27001, PCI DSS, and DORA.
https://qapp.mach41.com/board
Executive board view showing modelled dollar risk exposure, open cases, and SLA
CASE #Q-2026-0142 · SIGNED & CLOSED

Run the same workflow on your repositories.

Scan a repository of your choice to inspect signed case records, source-to-sink traces, and disproven metrics on your own code. Request a live walkthrough or workspace access below.

© Copyright MACH41 (UK) Ltd. All rights reserved.