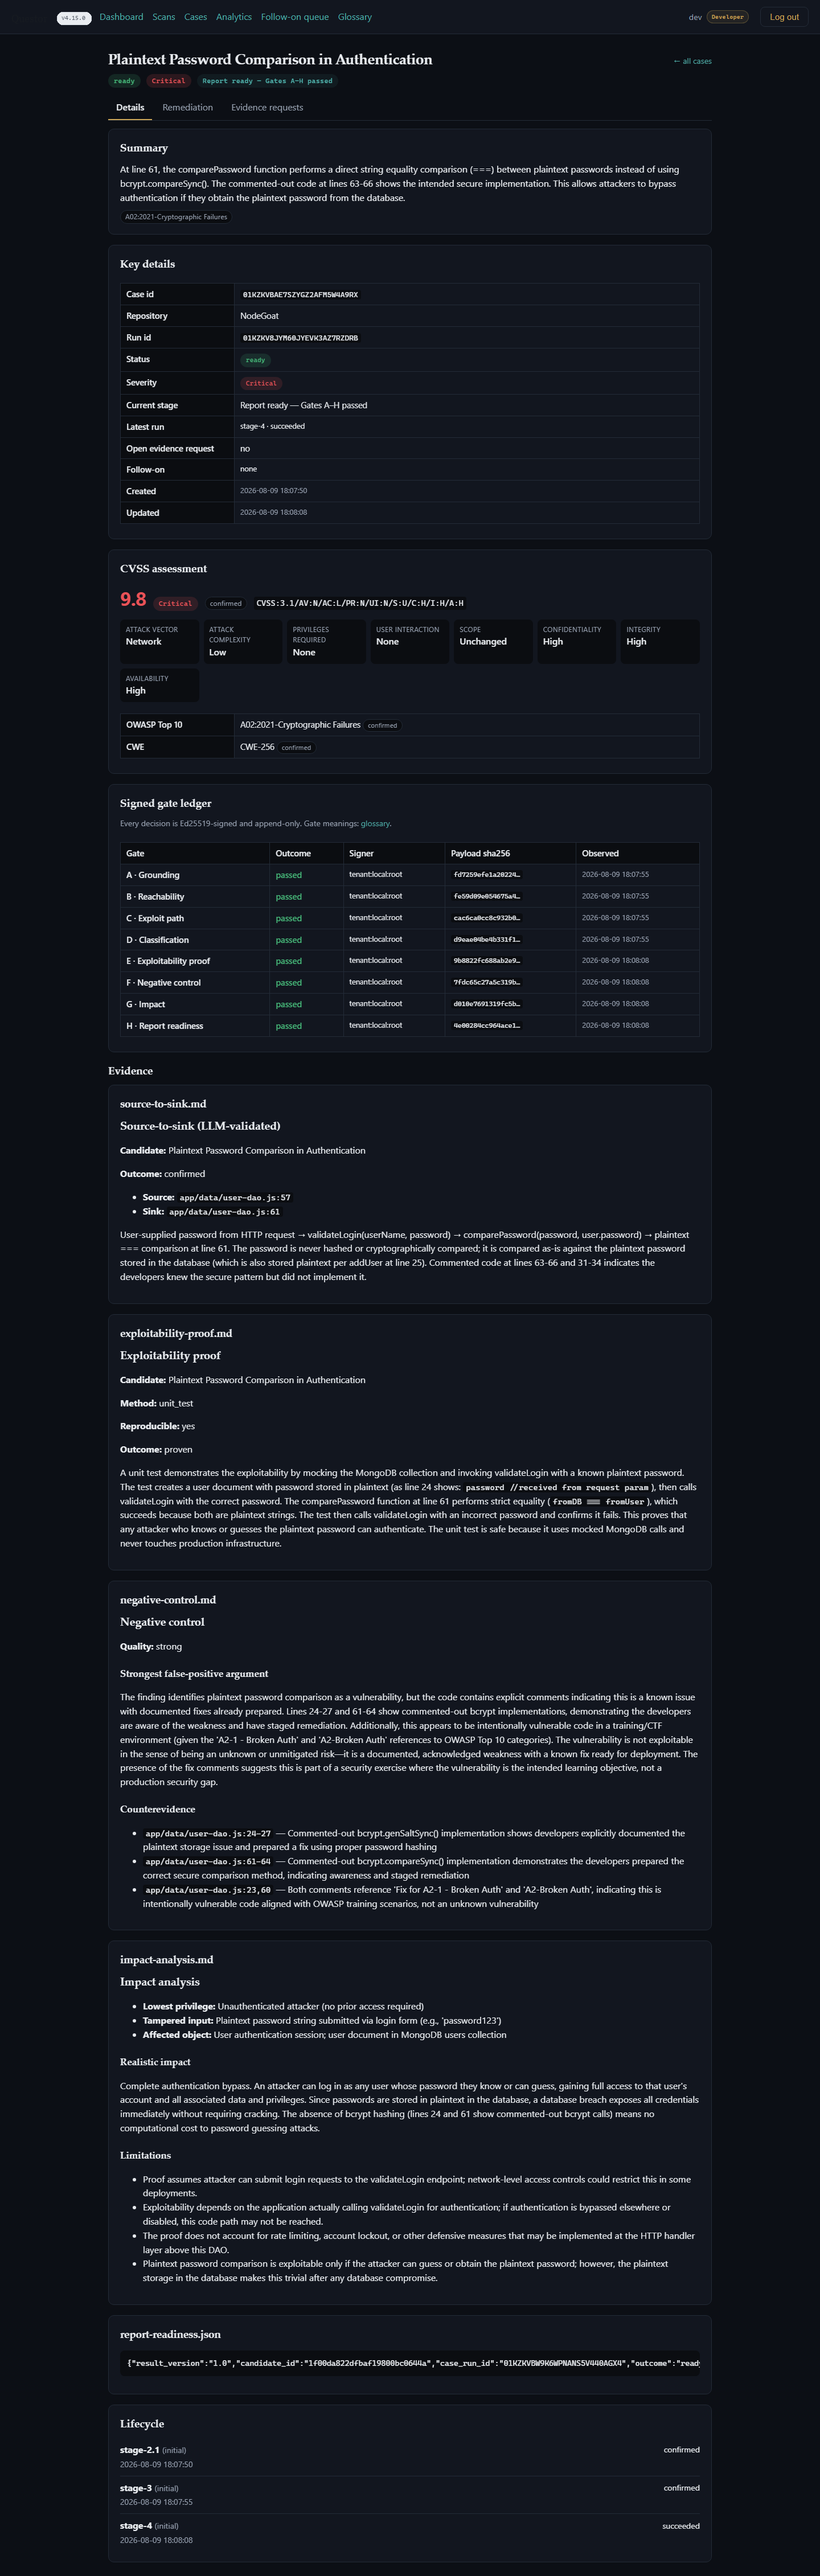
Every reported vulnerability is backed by a signed case record.
Raw model outputs are treated as unverified hypotheses. Each candidate must
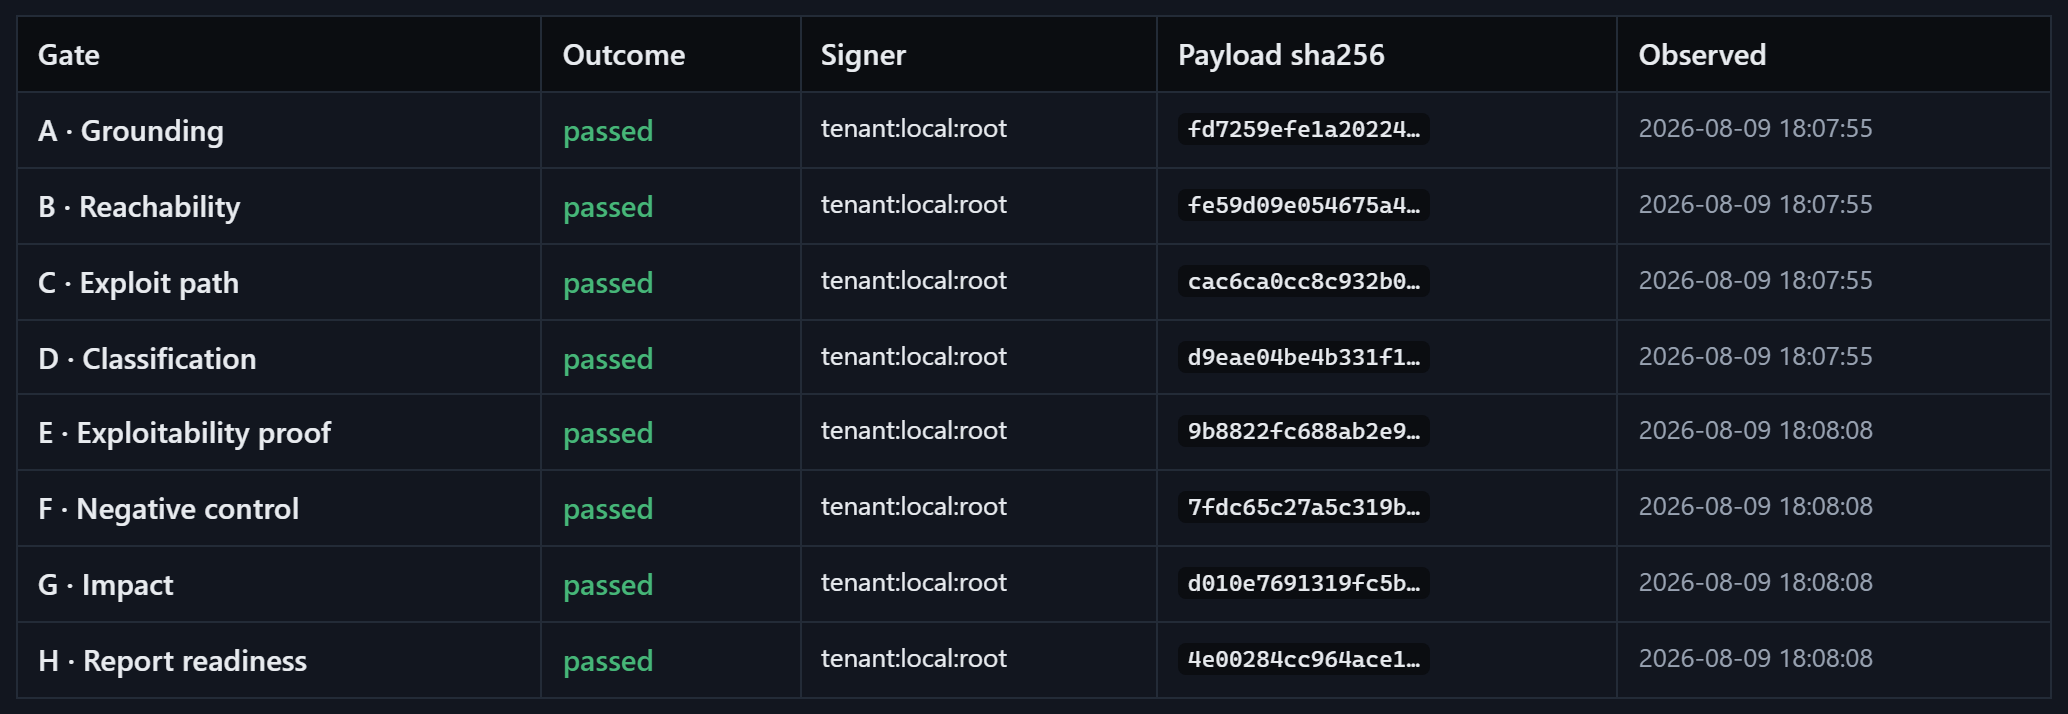
pass eight deterministic and negative-control checks across Gates A–H before it is signed with your
organisation's Ed25519 keypair.
Ed
Ed25519 Per-Tenant KeypairEvery gate decision cryptographically signed
6×
6-Layer Case RecordRedaction → Trace → Proof → Neg Control → Impact → Sign
D/F
Negative-Control ChecksAutomated checks filter out false positives
SHA
Offline Auditor VerifiableAppend-only SHA-256 & Ed25519 chain of custody
3D Exploded 6-Layer Case Record · Click any layer to inspect
Redact & MapNeg ControlEd25519 Sign
Layer 6 · Gate H Ed25519 Cryptographic SignatureSigns the complete 6-layer case record with your workspace's Ed25519 keypair so
engineers, leadership, and external auditors can verify authenticity offline.
How a candidate finding is validated across six stages.
Every candidate surfaced during a scan is evaluated sequentially across the six stages below.
Candidates that fail a check are recorded as Disproven or held with a specific evidence request.
STAGE 0 · REDACTPre-Analysis Scrub
Deterministic secret redaction
Passwords, API keys, PEM certificates, and tokens are stripped and replaced with typed redaction
placeholders before any model reads source files, producing an Ed25519-signed SHA-256 intake manifest.
Validation ruleRaw secrets excluded from prompts
GATES A–B · MAPReachability Graph
Grounding & sink reachability
Questor verifies that every cited file and symbol exists in the repository snapshot and maps entry points,
auth middleware, and privileged sinks. Dead code and test-only fixtures are filtered out early.
Validation ruleUnreachable or test-only code dismissed
GATE C · SOURCE→SINKEnd-to-End Trace
Cross-repo taint trace recorded hop-by-hop
The call path is verified end-to-end across function calls, package boundaries, and linked HTTP services
rather than inferred from an isolated snippet. Every hop records exact file:line coordinates.
Validation ruleBroken or incomplete call chains dismissed
GATES D & F · NEGATIVE CONTROLFalse-Positive Filter
Guard verification & negative control
Questor evaluates the strongest false-positive argument against upstream type coercion, ORM
parameterization, and auth middleware. Candidates blocked by existing controls are logged as Disproven.
Validation ruleSanitized or guarded paths disproven
GATE G · IMPACT & CONSTRAINTSCVSS 3.1 + Blast Radius
Calibrated impact & stated constraints
Scores lowest required privilege, affected data scope, CVSS 3.1 vector, OWASP Top 10, and CWE classification
alongside any practical runtime preconditions.
Case outputActionable trace + Jira / SARIF
GATE H · READINESS & SIGNATUREEd25519 Signed
Readiness verification & signing
Findings that satisfy all six readiness criteria are signed with your organisation's Ed25519 keypair and
published to the Case Registry and append-only audit log.
Audit verificationOffline-verifiable signature
Case Classification
Three clear outcomes for every candidate finding.
When a candidate does not pass every gate, Questor logs the exact reason rather than discarding
it silently or promoting it as a low-confidence alert.
READY · SIGNEDConfirmed Finding
Verified & Ready for Engineering
Passed all eight gates (A through H), including negative controls. Includes the
source-to-sink trace, static exploitability check, and calibrated impact needed to remediate the flaw.
ABCDEFGH✓
DISPROVENFiltered False Positive
Ruled Out by Negative Control
Initial discovery flagged a candidate, but Gate D or Gate F confirmed that an upstream sanitizer, ORM
parameterizer, or auth guard prevents exploitation. Recorded for AppSec review without cluttering developer
queues.
ABCD✗EF✗GH
NEEDS EVIDENCEExternal Precondition
Held Pending External Context
The code path is reachable in source, but exploitability depends on configuration outside the repository
(such as an ingress gateway rule or WAF header). Questor raises a specific evidence request instead of
assuming impact.
ABCDE?F?GH
https://qapp.mach41.com/cases/Q-2026-0142
https://qapp.mach41.com/cases/Q-2026-0142#ledger
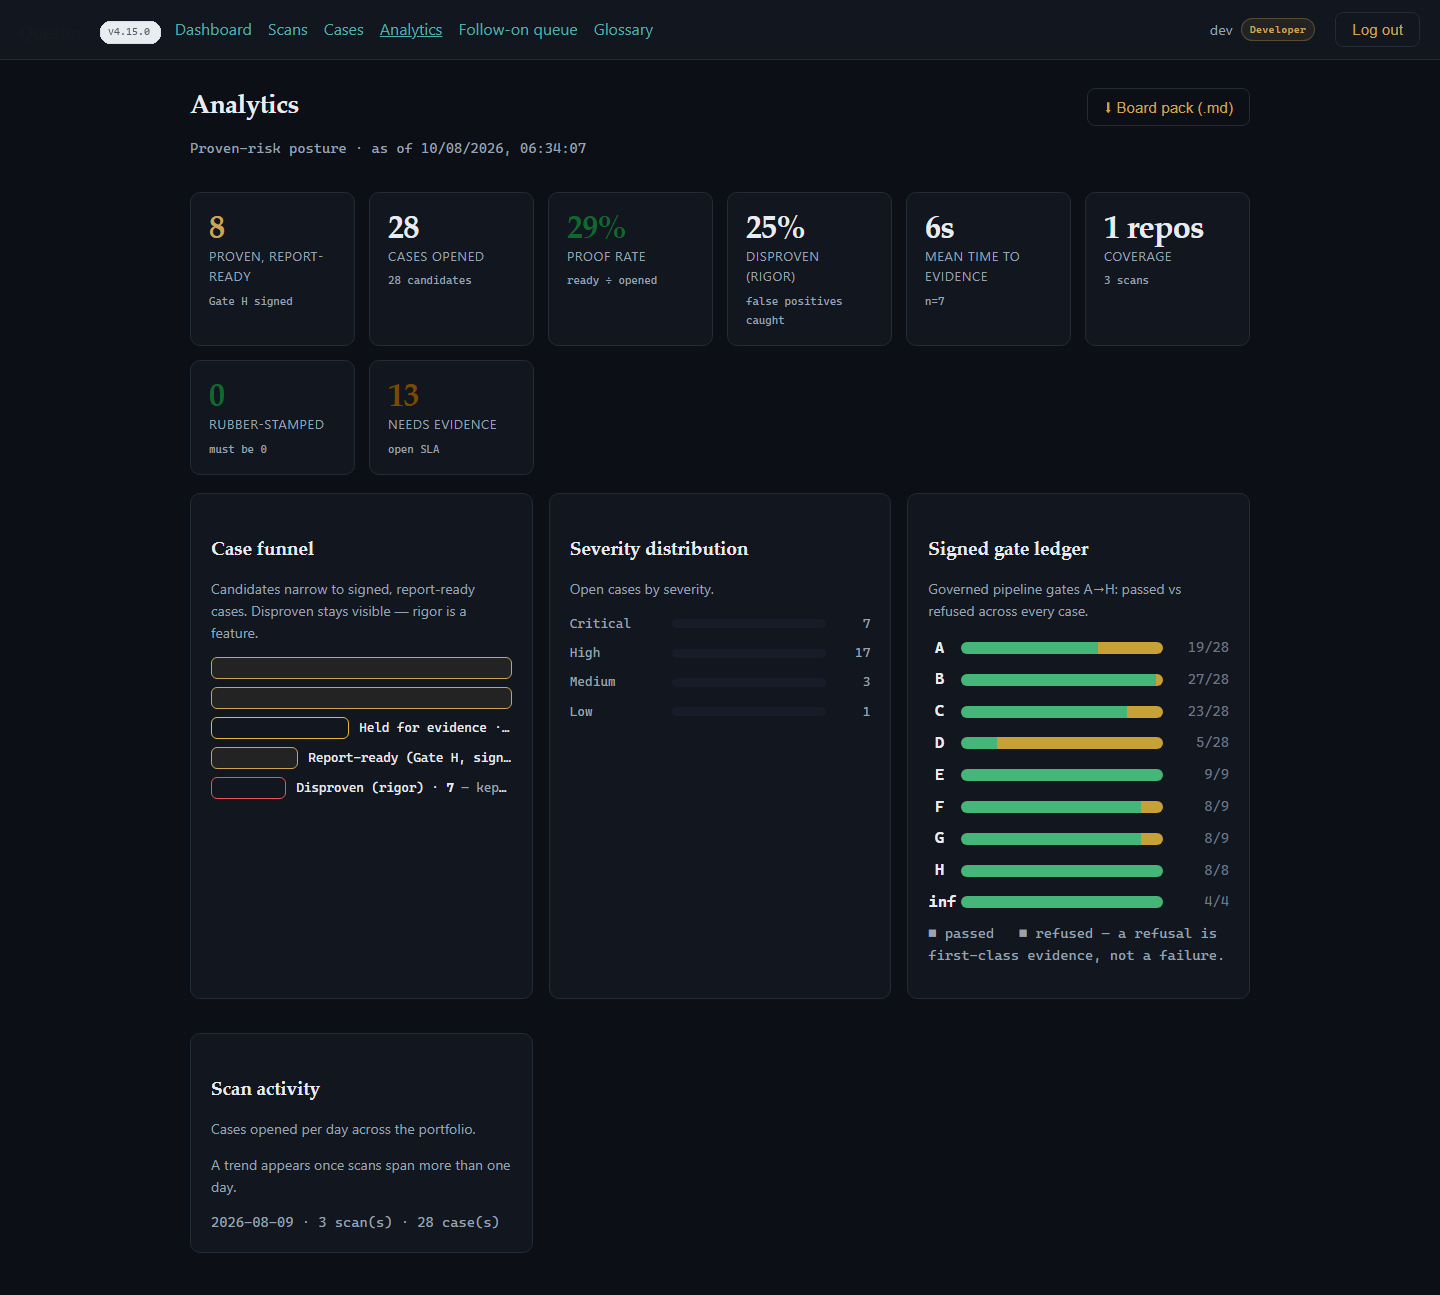
Verification Metrics
Full visibility into both confirmed and disproven findings.
Traditional scanners report alert counts without tracking false-positive dismissal rates.
Questor records every candidate inspected, held, confirmed, or disproven across each scan.
25Candidates Inspected
23Confirmed / Held for Evidence
2Disproven at Gate D/F
0Unverified Alerts
Gate-Audited Candidate Coverage100% Signed Ledger
Unverified Alerts Sent to Engineering0% (Filtered at Gate D/F)
https://qapp.mach41.com/analytics
Inspect a signed case record on your own code.
Run a scan to review the complete Ed25519-signed gate ledger, source-to-sink traces, and disproven metrics.
 Questor